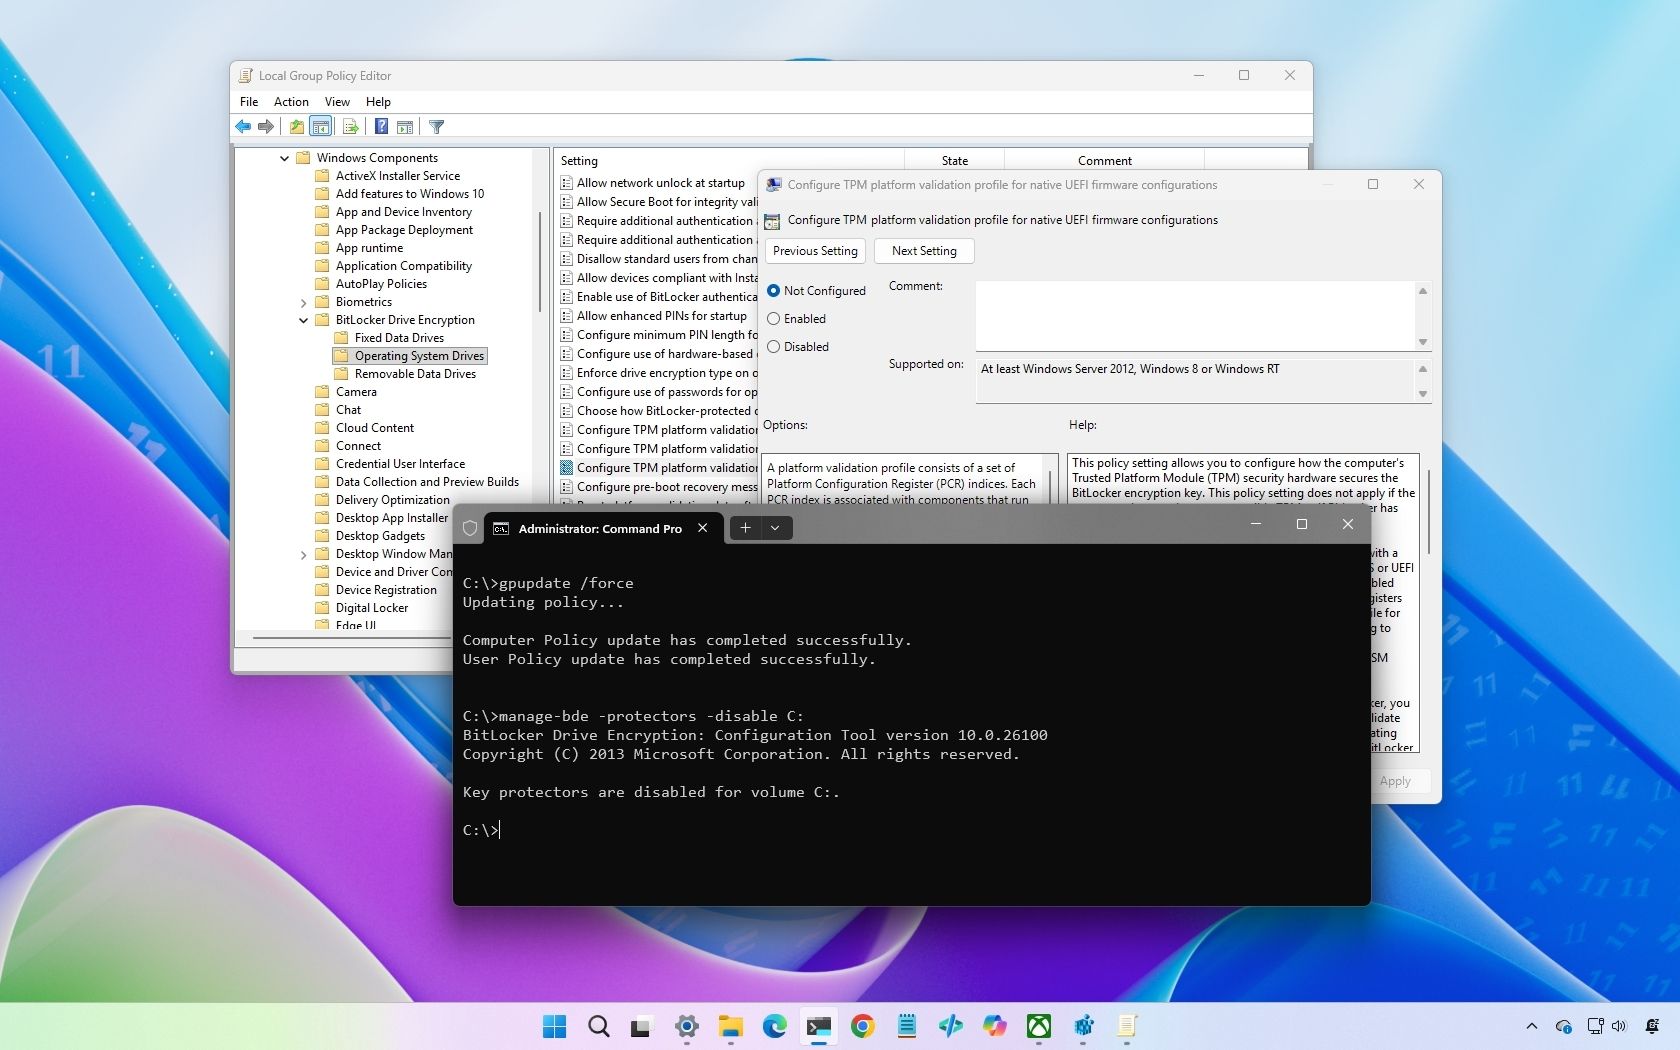
Microsoft issues mitigation for critical Windows 11 BitLocker flaw exploited with a USB key — “Can’t come up with an explanation beside the fact that this was intentional.”
Microsoft has issued mitigation measures for a critical BitLocker vulnerability in Windows 11 that allows attackers to bypass full disk encryption using a USB key. The zero-day exploit, dubbed YellowKey, was discovered and publicly documented by security researcher Chaotic Eclipse (Nightmare-Eclipse), who successfully demonstrated the ability to circumvent Windows 11’s encryption protections.
The vulnerability affects Windows 11, Windows Server 2022, and Windows Server 2025, though Windows 10 systems remain unaffected. The security researcher suggested the flaw may have been intentional, given the specificity of the vulnerability’s impact. While Microsoft has provided mitigation steps, the full technical details of how the exploit functions remain limited based on available information.